BLOG
AI Scams and Phishing in Thailand 2026: What Businesses Must Do
AI Scams Are Getting Better Faster Than Your Staff Can. Here's What to Do.
The scale of online fraud in Thailand is now hard to overstate. People in Thailand lost nearly THB 9 billion — around US$273 million — to online scam networks in the first half of 2026, across more than 170,000 reported cases (Nation Thailand, August 2026). The government’s response has been real: the Anti-Online Scam Operation Center closed more than 351,000 mule accounts and froze over THB 3.6 billion in illicit funds between late 2025 and mid-2026.
That crackdown is genuinely effective against high-volume consumer fraud — the SMS and call-centre scams aimed at individuals. But it does very little for the quieter, more expensive category of attack aimed directly at businesses. And those are the ones getting sharper fastest, because AI has removed the tell-tale signs staff were trained to spot.
Why business attacks are different
Consumer scams are high-volume and low-value: cast a wide net, catch whoever bites. Attacks on businesses are the opposite — patient, targeted and expensive. The attacker isn’t trying to trick one careless person out of a few thousand baht. They’re trying to compromise a company’s finance process, where a single successful move can be worth six figures. These attacks don’t appear in the scam-centre statistics, because they target your systems and your people directly.
Business email compromise: the quiet, expensive one
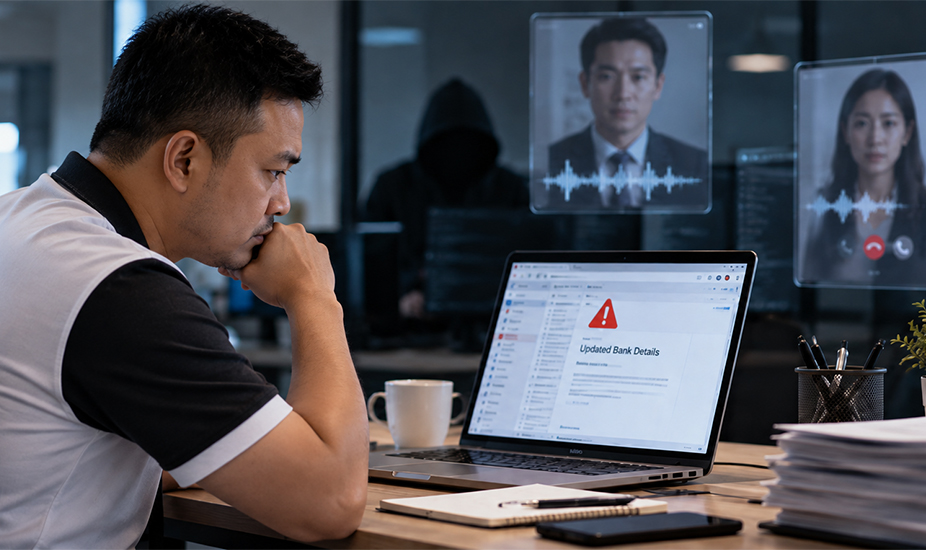
The most costly business attack rarely involves malware at all. In business email compromise (BEC), an attacker who has read your inbox for a few weeks learns who approves payments, how your invoices are phrased, and when your suppliers expect to be paid. Then they send a single, believable email — changing the bank account on a real invoice, or requesting an urgent transfer while the boss is “travelling.” No alarm sounds, no antivirus triggers. Just a wire transfer to the wrong account, discovered when the real supplier chases payment weeks later.
AI has removed the warning signs
The scam emails hitting Thai inboxes in 2026 are not the badly translated messages of a few years ago. AI now writes them — clean Thai grammar, believable sender names, plausible context drawn from real business relationships. The same technology produces deepfake voice and video convincing enough that Thailand’s anti-scam agencies have flagged it as a rising threat this year. A phone call that sounds exactly like your managing director asking for an urgent payment is no longer science fiction.
This matters because almost every piece of anti-phishing advice ever given to staff — “watch for bad grammar, check the sender, be suspicious of odd phrasing” — was built for a world where fakes looked fake. That world is gone.
Why training has a ceiling
Awareness training still has value, and every business should do it. But training has a hard ceiling: it depends on a tired employee spotting a well-crafted fake on a busy afternoon, and it does nothing at all for the message that arrives at 2am when nobody is looking. You cannot train your way out of a threat engineered specifically to look legitimate. Relying on training alone means your last line of defence is a human judgement call under time pressure — which is exactly what the attacker is counting on.
What actually closes the gap
Two things work where training runs out. The first is process: a simple, non-negotiable rule that any change to bank details or any unusual payment request is verified through a second channel — a phone call to a known number, not a reply to the email. This single habit defeats most BEC, because it breaks the attacker’s reliance on a single believable message.
The second is detection that doesn’t sleep. Continuous monitoring watches for the signals a human can’t — the unfamiliar login location, the mailbox rule that quietly forwards finance emails to an outside address, the admin session at 3am — and flags them regardless of the hour. Combined with multi-factor authentication, which stops most stolen passwords from working at all, this is the layer that catches a successful phish by its behaviour rather than by hoping someone noticed the email.
HumanIT’s Gold package delivers exactly that layer — 24/7 SOC-lite monitoring and alerting, access controls and user lifecycle operations — at THB 2,500 per device per month (THB 2,000 on annual billing). For a business that moves money by email, it is a fraction of the cost of a single successful transfer to the wrong account.
Frequently asked questions
How much are Thai businesses losing to online scams?
People in Thailand lost nearly THB 9 billion to online scam networks in the first half of 2026 alone, across more than 170,000 reported cases (Nation Thailand, 2026). Business-targeted attacks like BEC are a smaller but far more costly slice.
What is business email compromise?
BEC is an attack where a criminal uses access to, or knowledge of, your email to send a believable request — typically changing payment details on a real invoice or asking for an urgent transfer. It usually involves no malware, which is why antivirus doesn’t catch it.
Can’t we just train staff to spot scams?
Training helps but isn’t enough. AI now produces phishing with clean grammar and deepfake voice and video, removing the signs staff were taught to look for. You need verification processes and 24/7 monitoring to catch what training misses.
What’s the one habit that stops most payment fraud?
Verify any change of bank details or unusual payment request through a second channel — a phone call to a known number — before acting. It breaks the attacker’s reliance on a single convincing message.
Want detection that doesn’t sleep?
Call Eve on +66 89 354 9916 or review the Gold package at humanit.asia/pricing-and-plans.

